
A visitor record can move through an event operation in seconds: a guest registers online, receives a QR code, checks in at a kiosk, collects a badge, and may scan into a restricted meeting room. Each step improves organization, but it also creates information that must be handled with care. So, how are visitor records protected without slowing down arrival or creating extra work for the event team? Through a planned combination of limited data collection, controlled access, secure technology, and clear onsite procedures.
For corporate conferences, exhibitions, hospitality activations, and workplace visitor programs, protection is not a feature added after registration opens. It is part of the operational design. The right setup gives organizers the information they need to welcome guests, manage capacity, print accurate credentials, and maintain access control – without exposing records to people or systems that do not need them.
How Are Visitor Records Protected Throughout the Event Lifecycle?
Protection starts before the first guest enters their details. A well-configured registration workflow asks only for information that has a real operational purpose. For many events, that means name, organization, email address, attendance type, and selected sessions. If dietary needs, accessibility requirements, vehicle details, or identification information are required, they should be collected only when the service or venue genuinely needs them.
This approach matters because every additional field increases the amount of information the organizer must manage. A product launch with general admission does not require the same record set as a secure executive briefing or a facility visit. The registration form, approval process, badge layout, and access rules should reflect that difference.
Once details are collected, records should be protected while stored, transmitted, used, and eventually removed. That lifecycle includes online registration, attendee imports, onsite check-in, badge production, access scans, post-event reports, and retention or deletion. A gap at any one stage can undermine an otherwise well-run program.
Secure registration and data transfer
Online registration pages should use encrypted connections so information is protected while moving between the visitor’s browser and the registration environment. Event teams should also control how attendee lists are imported. Sending spreadsheets through personal email accounts or sharing unrestricted files across multiple vendors creates avoidable risk.
A better process uses a designated, access-controlled transfer method and keeps a clear record of the approved source file. Before the event, teams should remove duplicate columns, old lists, and unnecessary information. Clean data is easier to protect, easier to search, and less likely to produce a badge or check-in error.
Role-based access for the people running the event
Not every person on an event team needs the same view of visitor information. Registration managers may need to edit records and approve attendees. Front-desk staff may only need to search for a name, confirm registration status, and print a badge. Brand teams may need attendance totals but not individual contact details.
Role-based access applies these practical boundaries within the registration platform. It limits what each user can see and change based on their assigned responsibilities. This reduces accidental edits and prevents an unrestricted account from becoming the default solution for every onsite request.
Access should be reviewed before doors open, especially when temporary staff, agencies, venue personnel, or multiple departments are involved. Shared logins create an accountability problem. Named user accounts, appropriate permissions, and prompt removal of access after the event provide much stronger control.
Protecting Records at the Check-In Desk
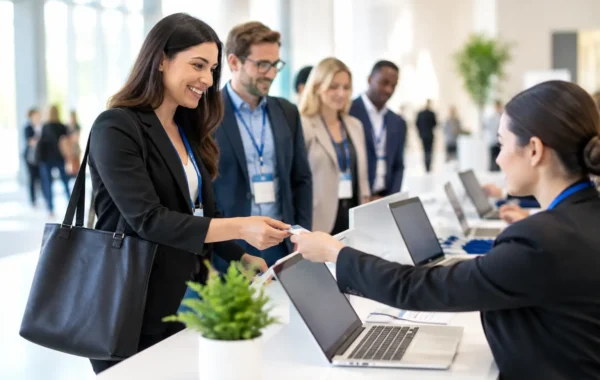
The check-in desk is where privacy controls become visible. A rushed welcome desk with open laptops, printed attendee lists, and untrained staff can reveal records even when the registration platform itself is secure. Physical setup and staff workflow matter as much as the software configuration.
Screens should be positioned so guests in line cannot read another visitor’s information. Devices should lock automatically when unattended, and staff should avoid announcing sensitive details across the counter. If a guest cannot be found, the team should verify their information discreetly rather than displaying a full list for everyone nearby.
Self-service kiosks need the same attention. A kiosk should clear the previous session before the next visitor begins, show only the information necessary to complete check-in, and be supervised by trained personnel during busy periods. This preserves fast throughput while preventing the next user from seeing the prior guest’s record.
Printed materials require control as well. An alphabetized paper list may seem convenient during a network interruption, but it exposes more information than a front-desk agent usually needs. If contingency lists are necessary, limit the fields, restrict who receives copies, collect them after use, and destroy them securely when they are no longer required.
Controls That Protect Digital and Physical Credentials
A visitor record often connects to a physical credential. Badges, QR codes, RFID cards, and NFC-enabled cards are useful because they speed entry, support attendance reporting, and help organizers manage restricted areas. Their design must balance convenience with information exposure.
A badge should display only what the event experience requires. A name, organization, attendee category, and visual access indicator may be enough. Personal contact details, registration IDs, or full access rules do not belong in visible print unless there is a specific operational reason.
For encoded credentials, the identifier on the card or code should point to a controlled record rather than openly carrying unnecessary personal data. If a badge is lost, a trained operator should be able to deactivate or replace it promptly. Access rules should also be configured around actual zones – for example, general event access, exhibitor access, speaker green room, or VIP reception – rather than granting broad permissions by default.
The core controls usually include:
- Encrypted data transmission between registration, check-in, and reporting systems
- Named accounts with role-based permissions for organizers and onsite staff
- Locked, supervised devices with session timeouts and restricted administrative access
- Minimal badge printing and carefully configured QR, RFID, or NFC credentials
- Defined retention periods and secure deletion of files, backups, and printed materials
These measures work best as one operating model. Encryption cannot compensate for a shared admin password, and a well-designed badge cannot protect a spreadsheet left open at an unattended registration counter.
Retention, Deletion, and Reporting After the Event
Visitor protection continues after the final guest leaves. Event organizers often need attendance reports for follow-up, lead management, certificate issuance, security documentation, or internal reporting. The question is not whether data can be useful after an event. The question is how long each category of data needs to remain available and who has a legitimate reason to use it.
Set a retention period before the event wherever possible. Registration data needed for marketing follow-up may have a different approved use and timeline from a venue access log or a visitor record collected for security. Clear ownership is essential: one person or department should be responsible for approving exports, managing retention, and confirming deletion when the period ends.
Reports should also be proportionate. A marketing team may need totals by company type, campaign source, or session attendance. They may not need an unrestricted export containing every field captured during registration. Limiting reports to the decision being made protects visitors and gives departments cleaner, more relevant information.
For organizations working across multiple venues or jurisdictions, privacy obligations can vary. That is why internal policy, venue requirements, contractual commitments, and applicable privacy rules should be reviewed before the registration workflow is finalized. High-security events, government-related functions, healthcare programs, and executive meetings may need additional controls, approval steps, or longer audit requirements.
Building Protection Into Event Deployment
The most reliable visitor-management setup begins with a practical briefing: what data is needed, who needs access, which devices will process records, where credentials will be used, and what happens when a guest needs help. From there, the provider can configure registration fields, staff permissions, kiosk behavior, badge templates, hardware layouts, and contingency procedures as one coordinated deployment.
Smart Track Zone supports this type of end-to-end execution by aligning onsite registration software, secure credential production, staged check-in hardware, and specialized onsite support. The result is not simply a faster entry line. It is a controlled visitor journey that protects operational information while presenting a polished, confident experience at every touchpoint.
The strongest test is simple: if a visitor asks how their information will be handled, the event team should be able to answer clearly, explain the purpose, and demonstrate that the process is intentional. That confidence starts long before check-in and remains part of the guest experience long after the event closes.